Lumma Campaign C++ Crypter
Reversing a multi-stage chain: an obfuscated C++ crypter hollows MSBuild.exe to run a dropper, which installs a .NET crypto clipper and a second crypter carrying Lumma Stealer.
Reversing a multi-stage chain: an obfuscated C++ crypter hollows MSBuild.exe to run a dropper, which installs a .NET crypto clipper and a second crypter carrying Lumma Stealer.
Reversing a Go loader that hides Lumma Stealer inside itself and injects it into explorer.exe.
Static and dynamic analysis of a multi-stage XWorm V7.1 delivery chain — from a spoofed MOHRE phishing email to a fully operational RAT injected into MSBuild.exe
Static analysis of an XWorm VBScript downloader — deobfuscation, payload extraction, and infrastructure analysis of a dead-C2 sample.
Hands-on reverse engineering of a multi-stage AgentTesla malware. Covers the complete loader chain, steganographic payload recovery, process hollowing, SMTP configuration extraction, and analysis of the final AgentTesla payload.
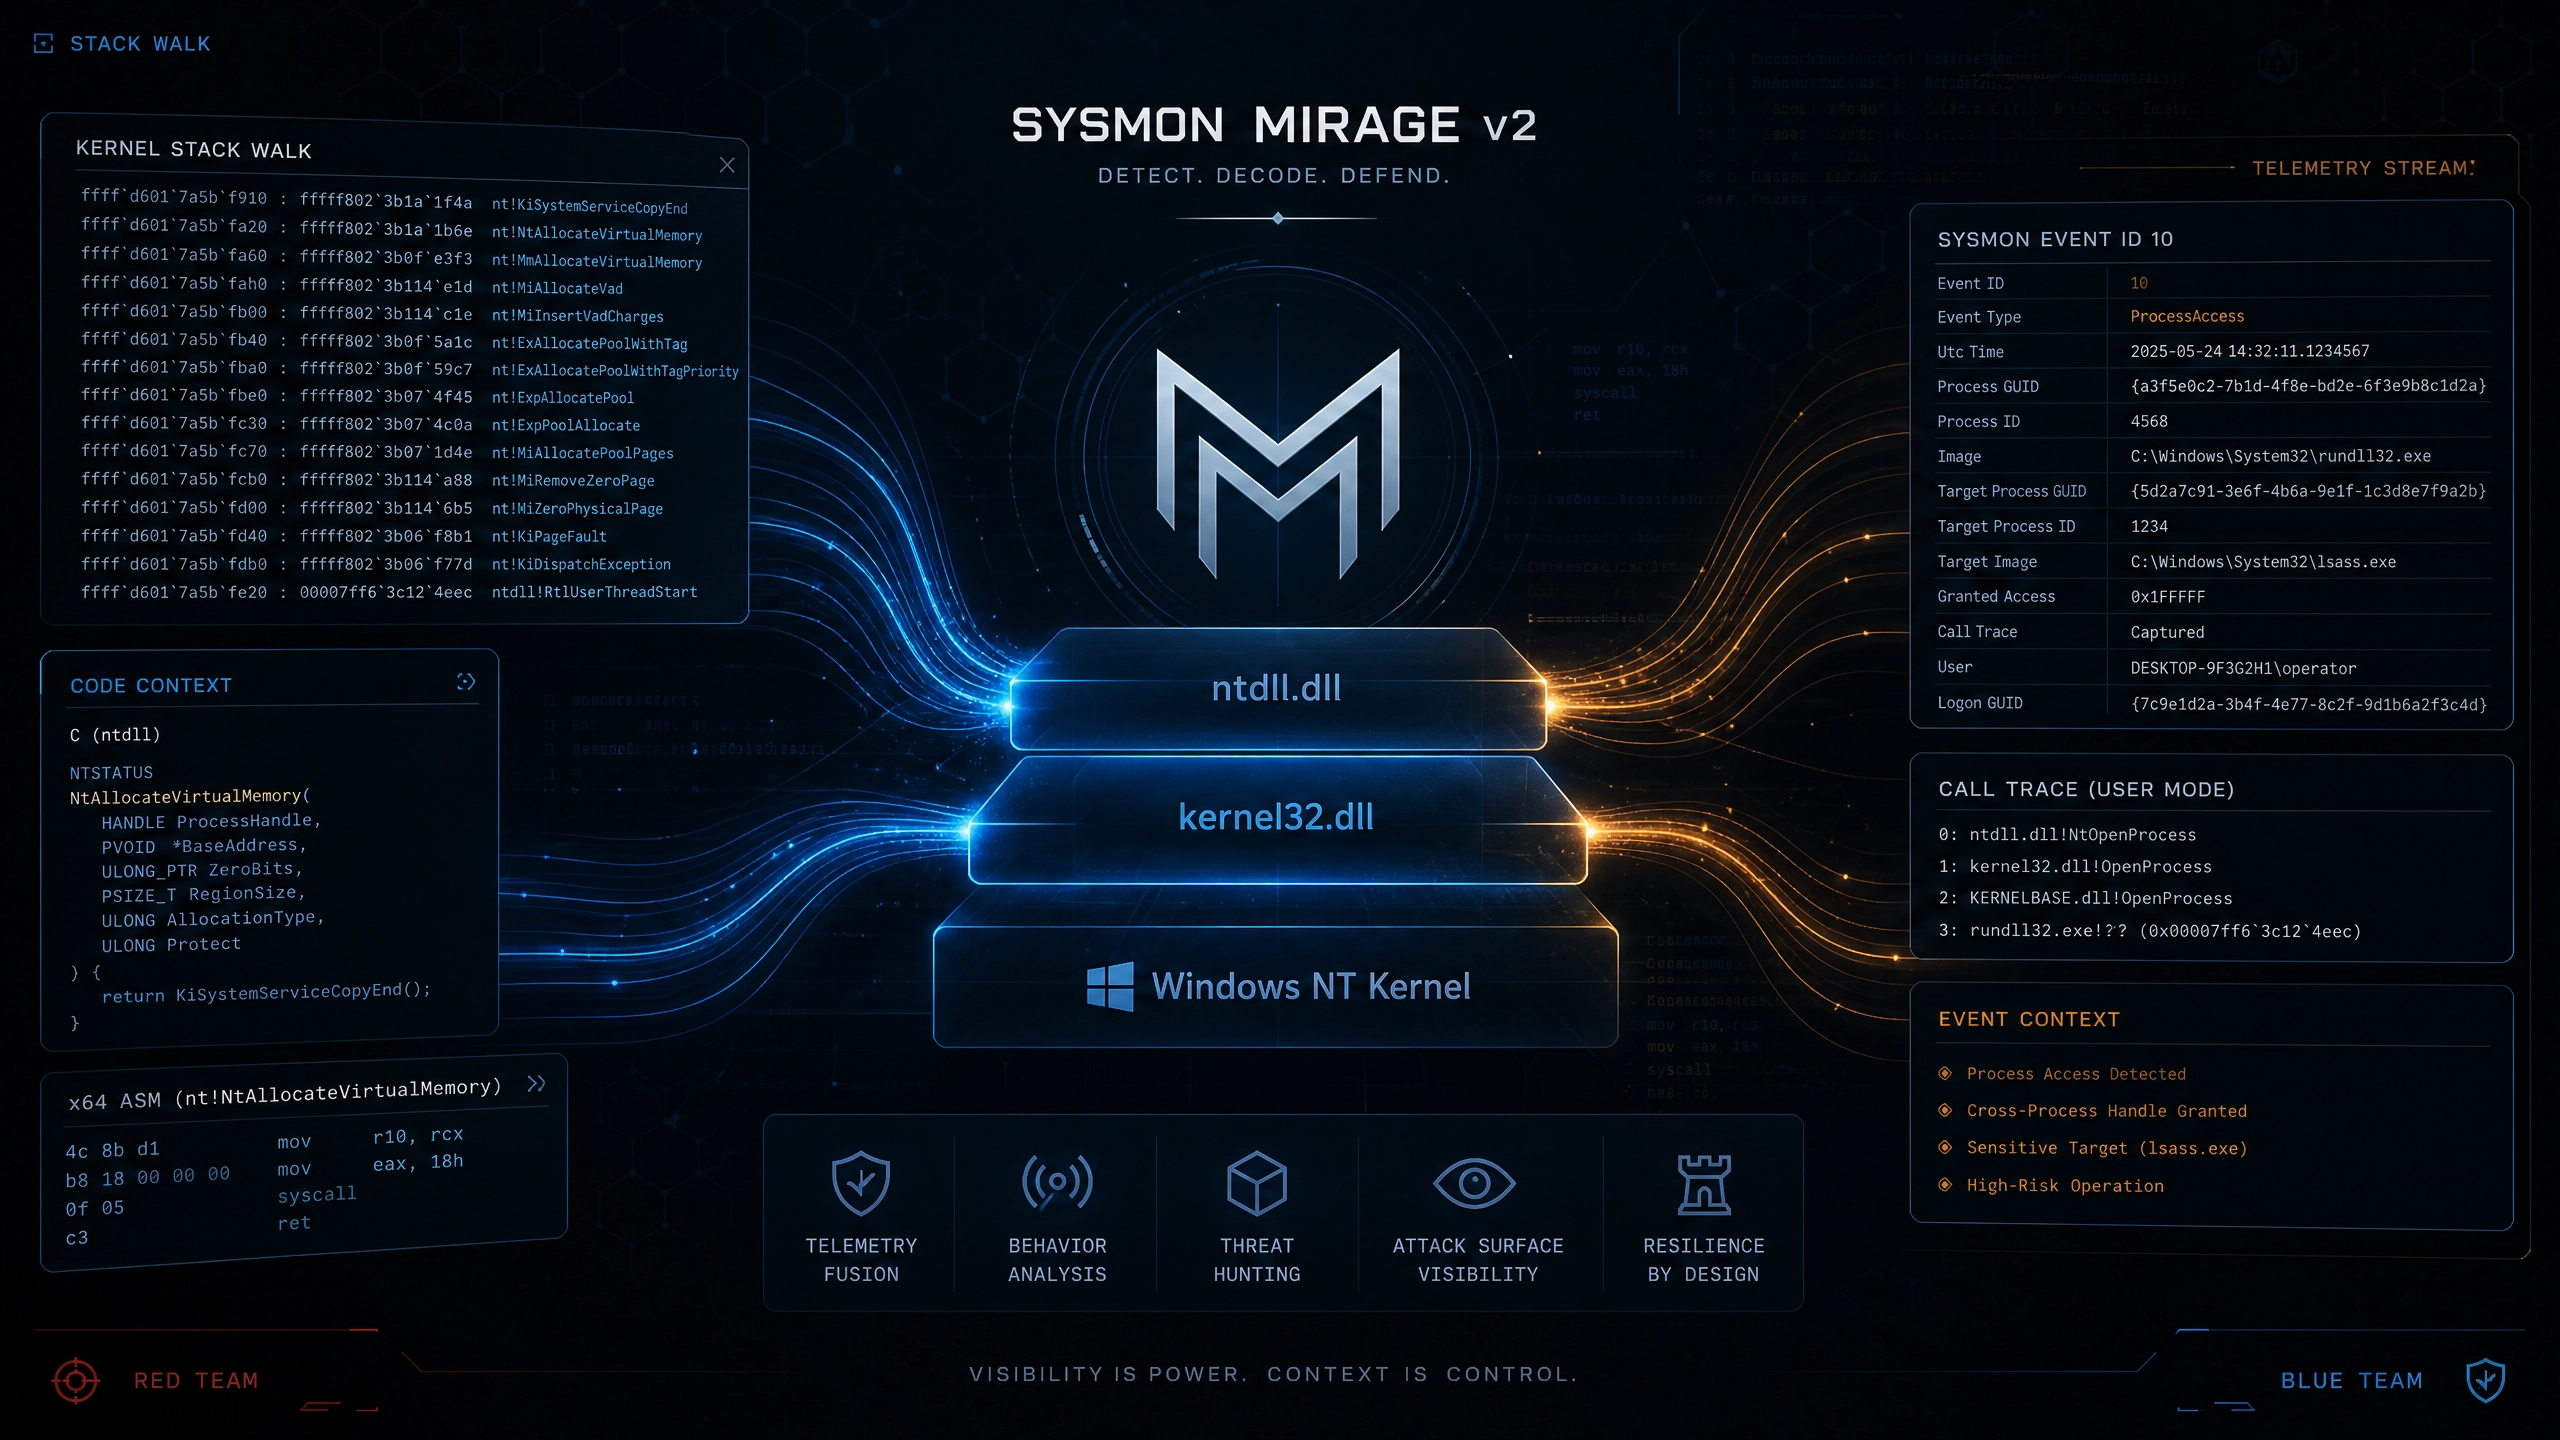
A controlled adversary emulation project covering three T1055 process injection techniques — Classic Win32 API, Direct Syscalls, and Indirect Syscalls — built from scratch in C and x64 Assembly.
A comprehensive guide to identifying and manually unpacking 64-bit UPX-packed binaries using 5 distinct reverse engineering techniques: Tail Jump, Memory Write, DEP Trick, Call Stack Backtracing, and Injecting Payload to an allocated memory.